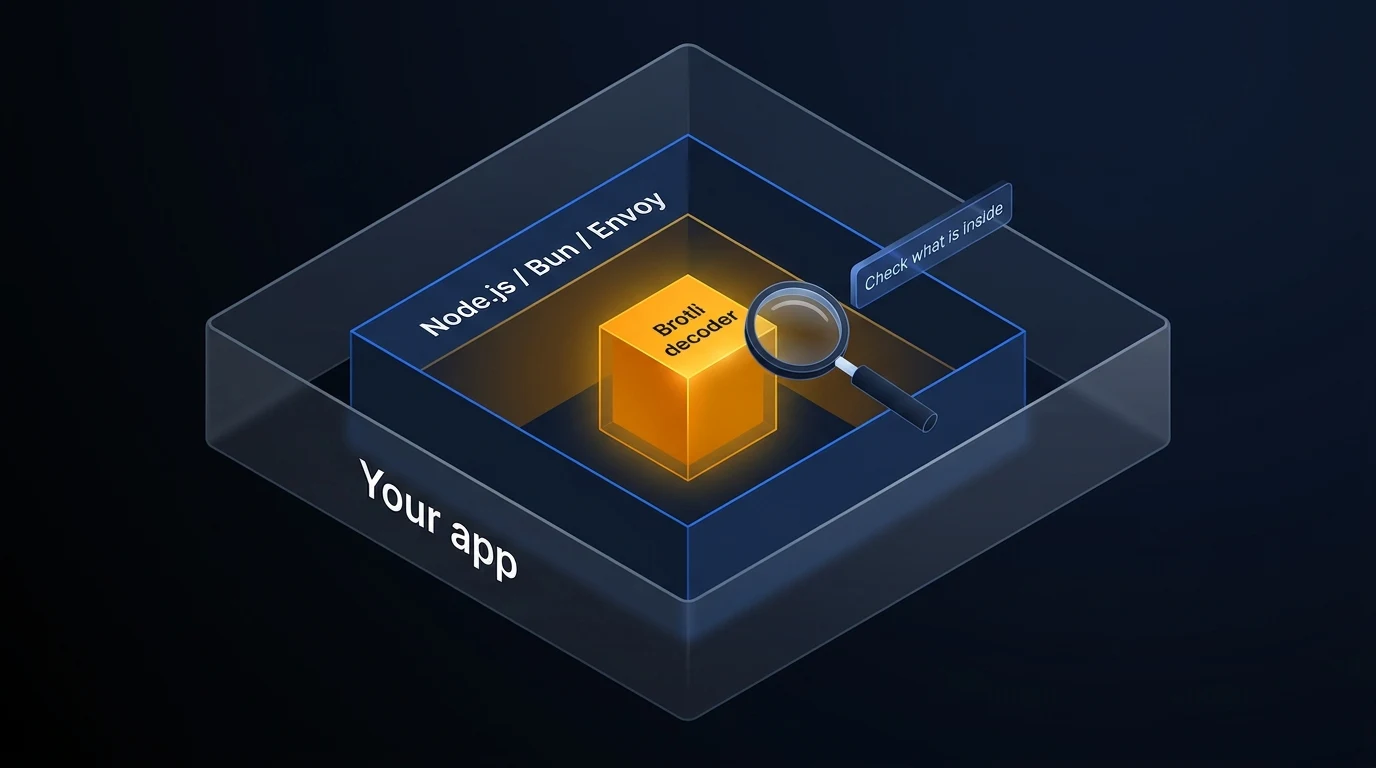
You updated every npm package last week. The lockfile is clean, and the audit report is green.
And your Node.js server is still vulnerable.
The reason is simple: the flawed code is not in your packages. It sits inside the runtime itself, as a private copy of a compression library you never chose. That is the lesson of the Brotli vulnerability, and it is why dependency checks have to go deeper than package lists.
Do This Today: A 6-Step Checklist
- Find your runtime versions: Check Node.js, Bun, Envoy or Istio, .NET, and Python Brotli packages on servers, in containers, in CI, and in build tools.
- Update to a fixed version: See the table below. Move off end-of-life Node.js lines.
- Rebuild what bundles a runtime: Containers, compiled executables, and desktop apps keep their own copies until rebuilt.
- Check Python: Update the
brotliandbrotlicffipackages. - If you cannot patch, reduce exposure: Disable Brotli decoding where possible, as covered below.
- Restart and verify: Confirm the running processes use the new versions.
What Brotli Is, and What Went Wrong
Brotli is a compression library from Google. It is widely used to shrink web traffic, and many programs bundle a copy of its decoder to unpack Brotli-compressed data.
| Item | Plain English |
|---|---|
| The flaw | An out-of-bounds write: the decoder can be tricked into writing past the end of a buffer |
| The trigger | Crafted Brotli-compressed data that the program decodes |
| The risk | A crash, a leak of process memory, or in some setups, running attacker-chosen code |
| Severity | 9.2 Critical (Google, CVSS 4.0). Node.js rates it High, and Red Hat rates it 8.1, Important |
Who Is Affected, and the Fixed Versions
| Software | Affected | Fixed | Notes |
|---|---|---|---|
| Google Brotli | 1.0.3 to 1.2.0 | 1.0.10, 1.1.1, 1.2.1 | The upstream library |
| Node.js | Unpatched 22.x, 24.x, 26.x | 22.23.4, 24.22.1, 26.12.1 | 18, 20, 23, 25 are end of life and get no fix |
| Bun | 1.0.21 up to 1.4.3 | 1.4.4 | Rebuild compiled executables |
| Envoy | 1.36.11, 1.37.7, 1.38.5, 1.39.2 | 1.36.12, 1.37.8, 1.38.6, 1.39.3, 1.40.0 | Only if Brotli decompression is configured |
| Istio | Branches using affected Envoy | See the Istio advisory | Only with Brotli decompression enabled |
| Python | brotli and brotlicffi packages | 1.2.1 and 1.2.1.0 | Fixed on PyPI |
| Others | .NET, PowerShell, and more | Vendor updates | Check each vendor |
When You Are Really Exposed
The flaw is in decoding, so what matters is whether your software decompresses Brotli data that someone else controls.
You may be exposed if:
- A Node.js app fetches content from servers you do not control and decodes Brotli responses.
- An application uses
node:zlibor Bun’s fetch to decompress Brotli. - An Envoy or Istio proxy is configured with the Brotli decompressor.
- A tool or service decompresses uploaded or downloaded Brotli files.
You are generally less exposed if:
- You only serve Brotli-compressed files to visitors, and never decode untrusted Brotli.
- Your Envoy setup does not have Brotli decompression turned on.
Check each case against your own setup. Exposure depends on how data reaches the decoder.
How to Check Your Versions
| Tool | Command | What to look for |
|---|---|---|
| Node.js | node --version |
Below 22.23.4, 24.22.1, or 26.12.1 needs updating |
| Bun | bun --version |
Below 1.4.4 needs updating |
| Envoy | envoy --version |
Compare with the fixed versions, then check for the Brotli decompressor in your config |
| Python | pip show brotli brotlicffi |
Below 1.2.1 (brotlicffi 1.2.1.0) needs updating |
Run these inside each container or build image too, not only on your laptop. The version a container reports is the one that matters for that service.
Why This Is a Dependency Problem
- Copies are bundled inside runtimes: Updating your npm packages does not update the Brotli code inside Node.js or Bun.
- Containers freeze old versions: A base image keeps the old runtime until you rebuild it.
- Desktop apps carry several copies: Electron-based tools can include Brotli in both the browser engine and the embedded Node.js runtime, and fixing one does not fix the other.
- The fix was quiet: Reports say a fix landed in Brotli’s source in February 2026 without being marked as a security fix, so scanners that watch for security labels could have missed it.
- End-of-life software has no safety net: No update is coming, so you must upgrade.
A Short Timeline
| Date (2026) | What happened |
|---|---|
| February 27 | A fix landed in Brotli’s source code, not marked as a security fix |
| October 21 | Fixed Brotli versions and Node.js security releases were published, and Node.js disclosed the flaw |
| October 22 | Advisories and fixes appeared for the Python Brotli packages |
| October 23 | Bun and Envoy published advisories |
| October 24 to 26 | Further vendors released updates, including Linux distributions, .NET, and PowerShell |
If You Cannot Patch Yet
| Measure | Why it helps |
|---|---|
| Disable Brotli decoding where you can | Removes the vulnerable code path from your traffic |
| Stop accepting Brotli from untrusted sources | Reduces how often attacker data reaches the decoder |
| Use a patched container image or distribution package | Gets the fix without waiting for your own upgrade |
| Isolate and monitor affected services | Limits damage if something goes wrong |
These are stop-gaps. Updating is the complete fix.
FAQs About the Brotli Vulnerability
What is CVE-2026-111497?
CVE-2026-111497 is an out-of-bounds write flaw in Google’s Brotli decoder. Crafted compressed data can corrupt memory and may lead to a crash, a leak, or code execution.
What is Node2Shell?
Node2Shell is a nickname for the Node.js side of CVE-2026-111497. The same flaw has also been called HTTP2Shell and Brotli2Shell as it was found in other software.
Which Node.js versions fix the Brotli vulnerability?
Node.js 22.23.4, 24.22.1, and 26.12.1. Node.js 18, 20, 23, and 25 are end of life and will not receive a fix, so upgrade to a supported line.
Is Bun affected by the Brotli vulnerability?
Yes. Bun versions from 1.0.21 up to 1.4.3 are affected, and Bun 1.4.4 fixes it. Rebuild any compiled executables that bundle Bun.
Is Envoy affected by the Brotli vulnerability?
Envoy is affected only if the Brotli decompressor is configured. Fixed versions include 1.40.0, 1.39.3, 1.38.6, 1.37.8, and 1.36.12. Istio is affected in the same case.
Do I need to turn off Brotli compression on my website?
Not because of this flaw. The issue is in decoding untrusted Brotli data. Serving compressed pages to visitors is different, but update any software that also decodes Brotli.
Is the Brotli vulnerability being exploited?
Researchers have demonstrated code execution on an unpatched Node.js build, and public proof-of-concept code exists. Treat unpatched, exposed systems as urgent.